Role-Based Access in Sports Software: A Club Guide
Published 5 November 2026

Role-based access in sports software means every person sees and does only what their role in the club requires. A head coach approves assessments, a parent sees their own child, an administrator manages billing, and nobody holds more power than the job needs. You set the permissions once per role, not once per person, and the system applies them whenever someone joins, changes job or leaves.
This guide shows how to design those roles for a club or academy, what US rules apply when children’s data is involved, how to review access, and what to check when your platform connects to other tools.
TL;DR
- Role-based access control (RBAC) groups permissions by role, so you manage a handful of roles instead of hundreds of individual accounts.
- Typical club roles are administrator, head coach, assistant coach, athlete, parent or guardian, scout and finance or store staff. Each gets a different view, edit and approve scope.
- For under-13s, US law (COPPA) requires verifiable parental consent before personal information is collected, so parent access and consent belong in your role design.
- Review accounts regularly, remove access the day someone leaves, and keep activity logs.
- Every integration (payments, store, email, video) is another way into athlete data, so give each connection the narrowest permissions it needs.
Table of Contents
- What role-based access means in a sports club
- Which roles a club or academy usually needs
- How to decide who can view, edit and approve
- Parents and guardians: what to consider
- US privacy rules when children’s data is involved
- Reviewing access, removing accounts and keeping logs
- Integrations: payments, stores, video and other club tools
- Perspective
- Running role-based access with LevelUp360HQ
- A rollout plan for your club
- FAQ
- Sources
What role-based access means in a sports club
The formal definition is short. NIST describes RBAC as a model that bases access decisions on users’ organisational roles, groups access rights by role and can limit people to the privileges their jobs need. The practical payoff, according to the same document, is easier administration: you update a role and everyone in it changes at once, with no need to edit each person.
In a club that matters because membership churns constantly. Volunteer coaches arrive in September and leave in May. Players move between age groups. Parents appear and disappear as children join and leave. If you grant permissions person by person, someone ends up with access they should not have, usually without anyone noticing.
A role has three parts:
- Who holds it: a coach, a parent, a treasurer.
- What they can see: which athletes, which fields (contact details, medical notes, ratings, video).
- What they can do: view, edit, approve, export or delete.
The third part is where clubs usually go wrong. “Can see” and “can change” are different permissions, and “can approve” is different again.
Which roles a club or academy usually needs
No single list fits every sport, but the same groups appear again and again. The table below is a starting point to adapt, not a standard.
| Role | Typically can | Typically cannot |
|---|---|---|
| Club administrator | Manage members, subscriptions, branding, staff accounts, payments | Alter an athlete’s assessed ratings without a coach’s record |
| Head coach or academy director | Approve assessments, manage sessions and syllabus, view all squad data | Change billing or payment settings |
| Assistant coach or volunteer | Run sessions, log attendance, submit assessments for approval | Approve their own submissions, see other squads’ records |
| Athlete (adult) | See and update own profile, view own card, take part in challenges | See other athletes’ private data |
| Parent or guardian | See their child’s profile, schedule, progress and bookings, give consent | See other children’s data, edit assessments |
| Scout or visitor | See athlete profiles that have been made visible to them | See contact details, medical or safeguarding records |
| Finance or store staff | Handle orders, event bookings, refunds | See performance or welfare notes |
Notice the split between submitting and approving. It is one of the most useful patterns in any club system.
Let governing-body categories shape your roles
Your sport’s governing body probably already sorts people by how much contact they have with young athletes, and your software roles should follow that logic. Under USA Gymnastics’ safe sport policy, effective 1 November 2021, adults with regular contact and/or authority over minor amateur athletes must pass a background check and the SafeSport core course before contact. USATF’s categories of adult participant include coaches, certified officials, club leadership, medical personnel, and contractors or vendors with athlete access.
The lesson for software is simple. A contractor who maintains your website is a different kind of person from a coach, and neither should get the default “staff” role by accident. Build a role for each category you actually have, and make screening status a condition for the roles that involve contact with minors.
How to decide who can view, edit and approve
Start from tasks, not titles. Write down what has to happen in a normal month: register players, run sessions, assess progress, collect fees, sell kit, answer parents. Then assign each task to the smallest group that can do it.
Separate the person who enters from the person who approves
NIST’s work on RBAC covers separation of duties: dividing tasks and privileges across several roles so that no single user holds excessive authority, which reduces the risk of fraud or serious error. In a club, that looks like:
- An assistant coach records a video assessment; the head coach approves it before it affects a player’s rating or tier.
- A volunteer processes a refund request; the treasurer authorises it.
- A parent requests a change to a child’s details; an administrator confirms it.
This protects young athletes from careless or biased scoring, and it protects staff from accusations, because the record shows who did what.
Use a short checklist for every new permission
- Does this role need this information to do its job this season?
- Is view-only enough?
- Could the same result be achieved with a summary instead of the raw record?
- Who approves changes made through this permission?
- What happens to the permission when the person leaves?
If you cannot answer the fifth question, the permission is not ready.
Keep roles few
Clubs that create twenty custom roles end up unable to explain any of them. Five to eight roles, plus the ability to limit a role to a squad or age group, covers most academies. Add a new role only when two groups truly need different access.
Parents and guardians: what to consider
Parents are the role clubs most often get wrong, either by giving them nothing and drowning in email, or by giving them too much.
The right approach is that a parent’s access is tied to a specific child, not to the club. One account may link to two children in different squads. A separated family may need two parent accounts with the same or different rights, and the club should follow whatever its records and any legal instructions say about each guardian.
For most families, a sensible default is:
- See: the child’s profile, schedule, attendance, progress and badges, and bookings or payments.
- Do: pay, book events, give or withdraw consent, update contact details.
- Not see: other children’s data, staff-only notes, assessment drafts awaiting approval.
Communication matters too. The U.S. Center for SafeSport’s minor athlete abuse prevention policies treat electronic communications as including email, texting, social media and video coaching, and require national governing bodies to limit one-on-one interactions between a minor athlete and an adult participant. If your platform has messaging, comments or a social feed, set who can message whom, and make sure parents can see what applies to their child. Check your own governing body’s current policy for the exact rule that applies to your sport.
US privacy rules when children’s data is involved
A sports platform that holds names, photos, ratings, video and contact details for children is handling personal information, and US law has specific requirements.
The Federal Trade Commission’s COPPA guidance says operators must get verifiable parental consent before collecting personal information from children under 13. For app-based notice and consent, the mechanism must be reasonably designed to make sure the parent actually receives the notice and gives consent. The same guidance notes that FERPA can apply where a platform stores educational records and acts as a school official, which is more relevant to school-linked programmes than to independent clubs.
Two practical consequences for role design:
- The parent role is a consent role. Under-13 athletes should not be able to complete their own sign-up in a way that bypasses the parent account.
- Retention needs an owner. The FTC says information collected from children should be kept only as long as reasonably necessary for the purpose it was collected, then securely destroyed. Decide which role can delete or anonymise a leaver’s record, and when.
This is general guidance, not legal advice. If you run a programme for under-13s, ask a lawyer familiar with COPPA to review your sign-up flow and retention policy.
Reviewing access, removing accounts and keeping logs
Good roles decay. People change jobs and nobody updates the system. Three habits stop that.
Review regularly. CISA’s identity and access management best practices for administrators call for periodically reviewing and reconciling accounts, and mention access reviews every 30 days or less. A volunteer club may not manage monthly, but a review at the start and middle of every season, plus whenever staff change, is a realistic floor.
Remove access promptly. The same guidance says to terminate or disable accounts and privileges when users separate or change role. In a club, build this into the leaving process: the coach hands back keys and kit, and loses system access the same day.
Keep logs. Activity logs let you spot suspicious behaviour, such as a coach exporting every squad’s contact list. Decide who can read the logs; it should not be the people being logged.
For admin accounts with the widest powers, the federal Privileged Identity Playbook recommends dedicated workstations with limited applications and internet connectivity for privileged tasks. A small club cannot replicate that, but the principle scales down: give administrators a separate, strongly protected login for admin work and use an ordinary account for everyday browsing and email.
If you want to see how another sport handles the administrative side of membership and booking rules, this piece on AI for golf-club administration shows the kind of controls clubs set around who may do what.

Integrations: payments, stores, video and other club tools
Most clubs run more than one system: a payments processor, a kit store, an email tool, a video library, maybe a membership database. Each connection moves data and, often, permissions.
Before switching an integration on, ask:
- What data flows, and in which direction? A store that only needs a name and shipping address should not receive a child’s ratings or medical notes.
- Whose permissions does the connection use? A connection running with full administrator rights is a standing risk. Prefer one limited to the task.
- Do roles carry across? If a coach cannot see billing in your main system, check they cannot reach it through a linked tool either.
- Who can switch it on or off? Make this an administrator-only action.
- What happens at exit? Find out how data is deleted from the linked tool when a child leaves, which ties back to the retention point above.
The cleanest setup is one platform where roles are defined once and apply to every module, so the rules for a parent are the same on the schedule, the store and the bookings page. Fewer separate logins also means fewer accounts to forget when someone leaves.
Perspective
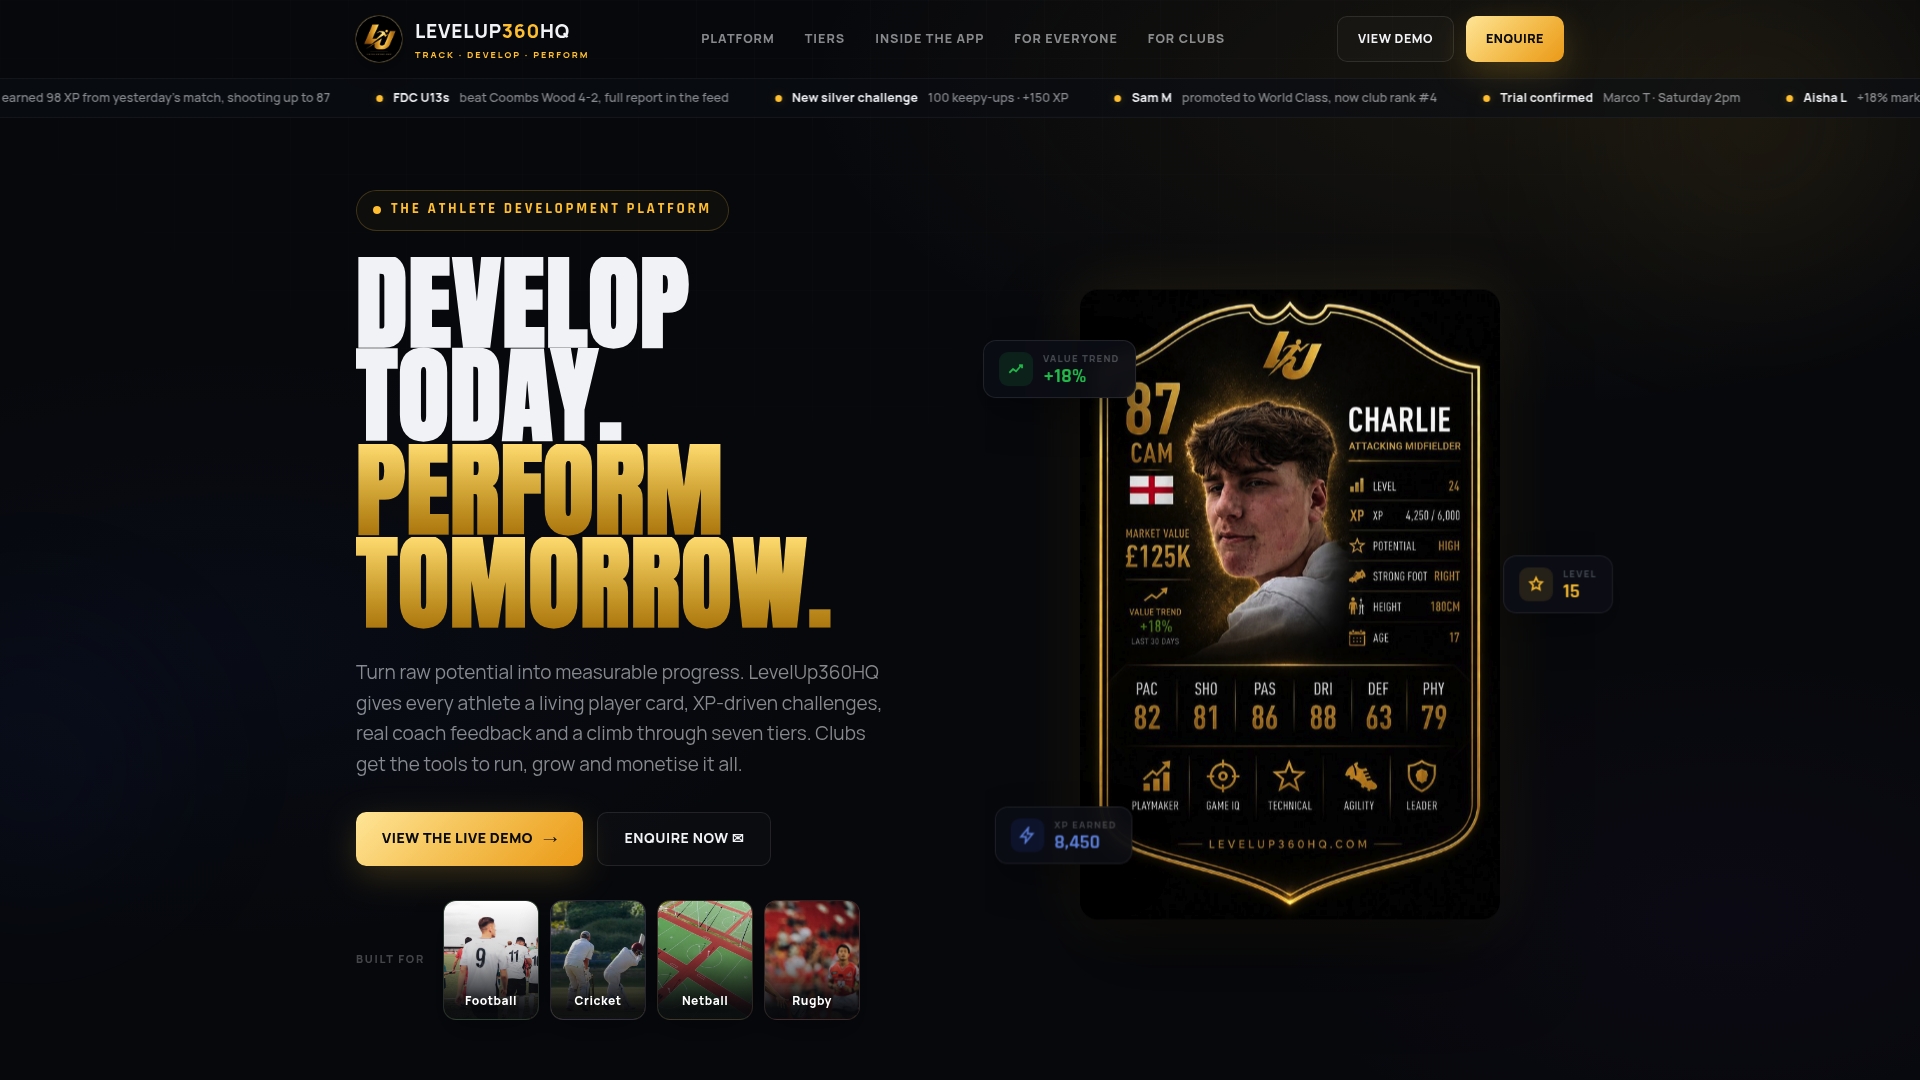
We built LevelUp360HQ around the idea that athletes, coaches, clubs and parents all need different windows onto the same development journey. An athlete owns a live player card and sees their own progress. A coach runs sessions, records video assessments and sends them through an approval workflow. A club administrator manages the programme, the branding, the subscriptions and the store.
Our view is that access design is part of youth safeguarding, not an add-on to it. When the people who can assess, approve, message and bill are clearly separated, clubs have a record they can stand behind and parents have a reason to trust the programme. That is why we design the platform to be highly configurable, with safeguarding built in, across football, cricket, netball, rugby and other sports.
If you are choosing software, judge it by how clearly it answers one question: who can see and change what, and who signs it off?
Chris
Running role-based access with LevelUp360HQ
LevelUp360HQ brings player cards, XP challenges, video assessments with approval workflows, session management, white-label club branding, CRM, subscriptions and store tools into one platform for clubs, academies, coaches, athletes and parents. Because those functions sit together, you can think about roles once for the whole club.
The Pro plan is £49 per month, with an active athlete platform fee of £1.50 per month per active athlete. Revenue share applies to integrated payments, and no price is published for it. See the details and the prototype on the LevelUp360HQ plans page, or start at the LevelUp360HQ home page.
A rollout plan for your club
- List your people. Group everyone who touches athlete data into categories, using your governing body’s definitions where they exist.
- Draft five to eight roles with view, edit and approve rights, using the table above as a template.
- Mark every approval point: assessments, refunds, changes to a child’s details.
- Set up parent links child by child, with consent recorded for under-13s.
- Restrict integrations to the narrowest data and permissions they need.
- Write the leaving process: who disables accounts, and how fast.
- Put reviews in the calendar: start of season, mid-season and after any staff change.
FAQ
What is the difference between role-based access and giving each person permissions?
With role-based access you define permissions for a role, such as head coach, and assign people to it. Changing the role updates everyone in it. Per-person permissions are slower to manage and more likely to leave someone with access they should have lost.
Should coaches see every athlete in the club?
Usually not. Limit coaches to the squads or age groups they work with, and give the head coach or academy director the wider view. This follows the principle of giving people only the privileges their jobs need.
Do parents need their own accounts?
Yes, for children’s data it is the safer pattern. A linked parent account lets the club record consent, show the parent only their own child’s information and remove access cleanly if circumstances change. For under-13s, COPPA requires verifiable parental consent before personal information is collected.
How often should a club review who has access?
CISA’s guidance mentions reviews every 30 days or less for organisations managing access formally. For a volunteer-run club, reviewing at the start and middle of each season and whenever someone leaves or changes role is a practical routine.
Sources
- NIST: Assessment of Access Control Systems
- NIST: The NIST Model for Role Based Access Control
- USA Gymnastics Safe Sport Policy
- USATF categories of individuals
- U.S. Center for SafeSport: Minor Athlete Abuse Prevention Policies
- FTC: Complying with COPPA FAQ
- FTC: Health data and COPPA
- CISA: Identity and Access Management Best Practices
- IDManagement: Privileged Identity Playbook
- AI for golf-club administration
Turn potential into a player card.
LevelUp360 tracks every match, builds your child's player card, and shows their development over time.
Get started free